Mail merge allows you to combine a message template with a structured data source to create personalized communications at scale. Mail merge works...

Key Takeaways
Greylisting is a classic receiving-server defense: temporarily refuse unfamiliar connections and see whether the sender behaves like a real mail system. In campaign delivery, that usually means a delayed first message. In email validation, the same 4xx response can quietly inflate “unknown” rates if the verifier does not wait and retry.
Anti-greylisting technology, in the DeBounce sense, is that retry logic — deliberate pauses and rechecks when a mailbox provider greylists a probe. This [2026] guide explains how greylisting works, why validators need it, how DeBounce uses it to reduce false unknowns, where SMTP still sets hard limits, and when results should stay uncertain on purpose. For the receiving-server perspective, see What Is Greylisting and How Does It Work?.
Greylisting (also spelled graylisting) is a defense used by some mail transfer agents (MTAs). When a message arrives from a sender–recipient–IP combination the server does not recognize, the server issues a temporary rejection (SMTP 4xx) instead of accepting the mail or permanently rejecting it with a 5xx.
If the sender is a properly configured mail server, it queues the message and retries after a delay — often several minutes to about half an hour, depending on the receiver. On a successful retry after enough time has passed, the message is accepted and that combination may be remembered so later mail is less likely to be deferred.
The original idea was simple: many early spam systems fired once and moved on. Legitimate MTAs retried. Greylisting is less decisive against modern spam infrastructure that also retries, but it remains one layer in some receiving stacks. It still affects first-contact delivery and — critically for list hygiene — SMTP-based validation probes.
Greylisting does not mean “your email is spam.” It means “we do not recognize this connection yet — come back shortly.”
Typical greylist signals during a check include temporary failure codes and deferral language such as “try again later,” “greylisted,” or similar policy text. Exact wording varies by provider. What matters for validators is the class of response: temporary, not permanent.
Filters have grown far beyond early greylist heuristics — reputation, authentication, content analysis, and engagement signals all matter more than they did a decade ago. That does not make greylisting irrelevant for operators who clean lists before they send.
First-contact and low-volume SMTP sessions still get deferred on some domains. Validation probes are often exactly that: short, unfamiliar, non-campaign connections. A single-pass mailbox check that treats every 4xx as “unknown” will systematically under-resolve addresses on greylist-prone hosts.
For senders, greylisting shows up as delayed first delivery to certain inboxes. For validators, it shows up as inconclusive results unless retry logic is built in. Understanding both views helps you interpret a cleaning report without assuming every unknown is a dead mailbox.
SMTP mailbox verification typically opens a conversation with the receiving server and asks whether a recipient can be accepted — without sending a full marketing message. That probe can hit the same greylist window a first-time campaign would.
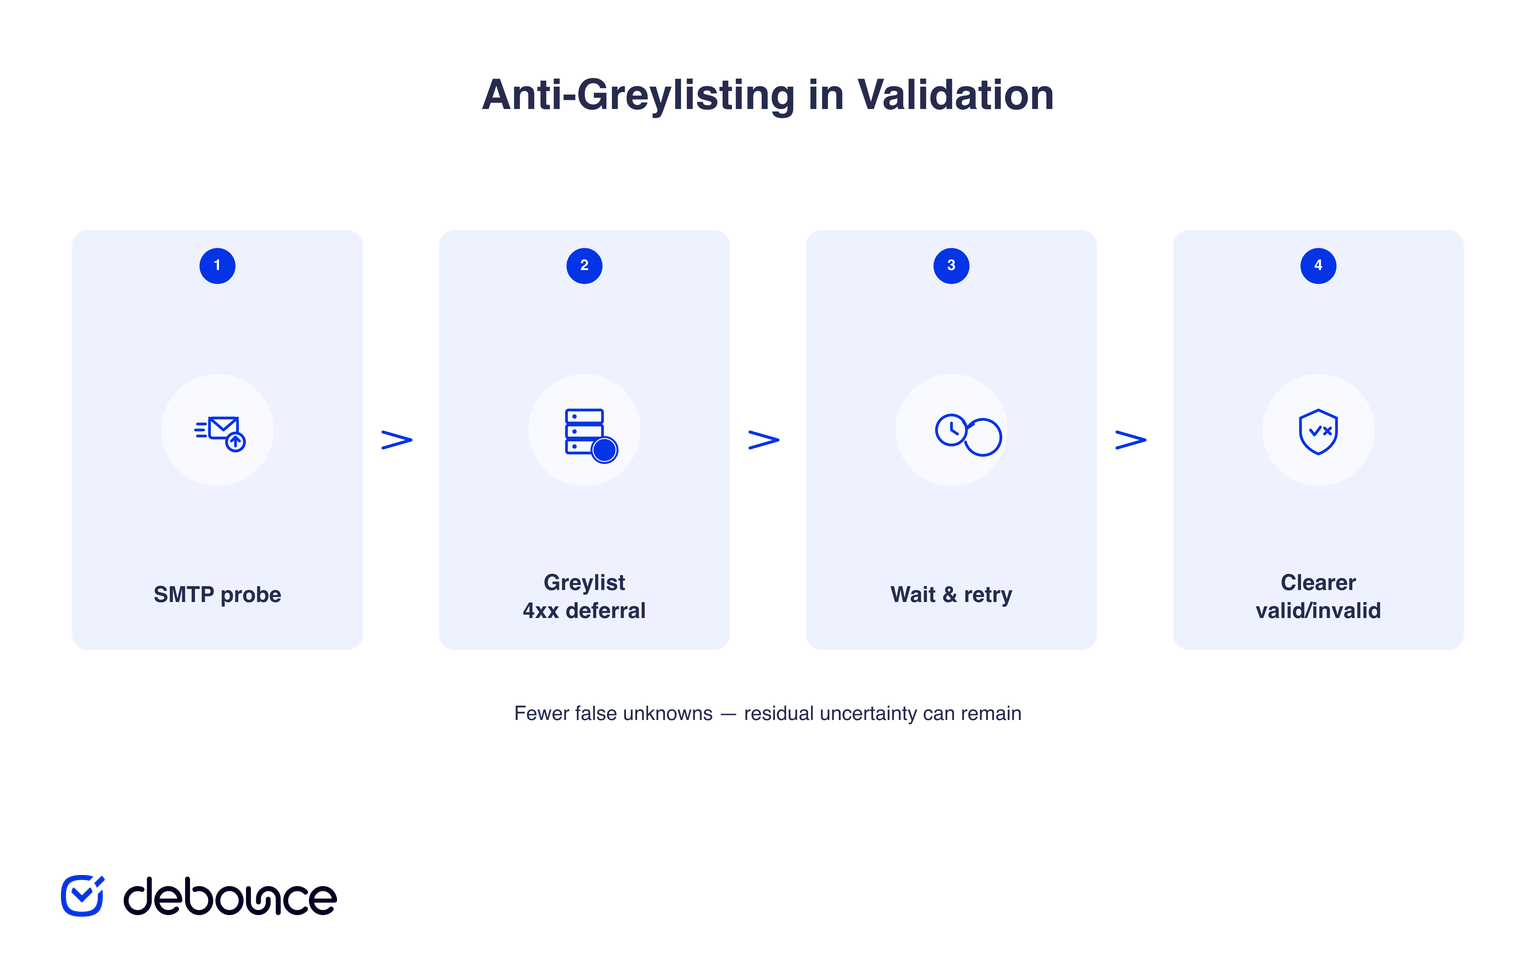
Without retries, the sequence looks like this:
That mix is the problem. “Unknown” should mean residual uncertainty after a reasonable check — not “we left before the greylist window closed.” False unknowns push teams toward bad choices: over-suppressing good contacts, or ignoring the unknown bucket entirely and sending into risk.
Retry logic mirrors how a well-behaved MTA works: wait, try again, and only then decide. That is the core of anti-greylisting in validation. It costs time. It buys clearer valid/invalid outcomes on addresses that were only deferred, not rejected.
In general email operations, “anti-greylisting” can mean any practice that helps legitimate mail get through temporary deferrals — for example, correct retry queues on the sending MTA.
In email validation, the meaning is more specific: when a verification attempt is greylisted, the validator does not immediately treat the address as failed or unknown. Instead, it waits and retries the check in a way that resembles a well-behaved mail server.
Anti-greylisting in validation uses deliberate pauses and retries between SMTP checks to reduce false “unknown” results caused by temporary greylist responses.
That is not the same as bypassing spam filters, spoofing trusted senders, or forcing delivery of campaign mail. It is patience and protocol hygiene applied to mailbox checks so temporary deferrals are less likely to pollute your results.
Most greylisting is time-based. The receiving server asks the sender to try again later. Delay windows vary by provider — commonly somewhere between about 1 and 30 minutes per encounter.
When DeBounce encounters greylisting during validation, it waits (on the order of ~30 minutes) and retries those specific addresses. You may wait longer for the job to finish, but you typically get fewer inconclusive results than a single-pass check would return.
Practical expectations:
If your list includes many corporate or regional domains that still greylist unfamiliar SMTP clients, this retry path is often the difference between a noisy unknown column and a report you can act on. Pair it with the rest of your hygiene stack — invalid removal, disposable handling, and a policy for accept-all addresses — rather than treating retries as a complete deliverability program. For accept-all and residual unknown handling, see keep or delete accept-all and unknown emails.
Anti-greylisting addresses one failure mode: temporary deferral mistaken for inconclusive. SMTP-based verification still has structural limits that retries do not erase.
Catch-all (accept-all) domains accept mail for almost any local part at the SMTP level. A successful RCPT response does not prove a human mailbox exists. Retries do not fix that ambiguity; they only confirm the domain’s accept-all behavior again.
Throttling and rate limits can return temporary errors that look similar to greylisting but are really “slow down.” Aggressive rechecking can make results worse, not better. Careful spacing matters.
Tarpitting and intentional delay stretch the conversation to frustrate abuse. A validator may eventually get a response — or may still time out depending on policy and patience settings.
Policy blocks and reputation filters can refuse probes with permanent or semi-permanent responses unrelated to whether the mailbox exists. Waiting does not turn a policy refusal into a valid/invalid mailbox fact.
Greylisting that never clears for probes happens on some hosts that treat verification traffic differently from normal queued mail. In those cases, unknowns can remain after retries — and that remaining uncertainty is honest.
Understanding these limits keeps expectations realistic: anti-greylisting reduces one class of false unknowns; it does not make SMTP omniscient.
A mature validation workflow does not force every row into valid or invalid. Some outcomes should remain uncertain so you can apply a risk policy instead of inventing certainty.
Keep uncertainty on the table when:
What to do with residual unknowns depends on your channel. High-stakes cold outreach often suppresses or segments them. Warm lifecycle programs may keep engaged unknowns under tighter monitoring. Ecommerce and product signup flows often push verification earlier — at capture — so greylist-prone checks are less likely to surprise you on send day. Soft product path: use DeBounce list cleaning or API checks where clearer SMTP outcomes matter, and document how your team treats leftover unknowns.
The point is decision quality. Anti-greylisting helps you shrink the false-unknown slice. Honest uncertainty on the rest beats a false “valid” that later bounces.
It is useful to separate two ideas:
For validators: retrying after a temporary deferral is normal SMTP behavior. That is what anti-greylisting automation does.
For marketers sending campaigns: the healthy approach is not to defeat receiving servers. It is to look like a trustworthy sender so greylisting is rare or short-lived: authenticated domains, consistent volume, low complaints, and clean lists.
Whitelists and reputation systems on the receiving side can reduce greylisting for known good senders. Those are receiver-controlled controls, not something you “turn off” from the outside. Confusing validation retries with delivery tricks leads to the wrong investments — and the wrong expectations when a report still shows unknowns.
These practices will not eliminate every temporary deferral, but they reduce how often new connections look risky:
Authentication and list hygiene work together. A clean list with weak authentication still struggles. Strong authentication with a dirty list still generates bounce and complaint signals. Greylist friction often shrinks when both sides improve.
If a validator returns a large share of “unknown” results, greylisting (or similar temporary SMTP policies) may be part of the story. Anti-greylisting retries trade time for clearer outcomes on those addresses.
That still sits alongside other hygiene work: removing confirmed invalids, handling disposables, monitoring list decay, and applying a risk policy for catch-all domains. Validation reduces uncertainty; it does not replace permission-based acquisition or authentication.
When you compare cleaning vendors or in-house scripts, ask what happens on 4xx greylist responses. A fast job that skips retries can look efficient and still leave you with an inflated unknown pile. A slightly longer job that waits and rechecks often produces a report you can segment with more confidence — while still leaving true edge cases marked uncertain.
Greylisting temporarily defers unfamiliar senders to test whether they behave like real mail servers. Anti-greylisting technology in email validation mirrors that retry behavior so greylisted probes are less likely to end as inconclusive unknowns. Expect longer processing when greylisting appears — and cleaner results when the retries complete.
SMTP still has limits. Catch-all domains, throttles, tarpits, and policy blocks can leave honest uncertainty on the table. Use retries to reduce false unknowns, then apply a clear risk policy to whatever remains.
If you are validating a list and care about fewer greylist-driven unknowns, use a validator that retries deliberately — DeBounce builds that patience into mailbox checks — keep your own sending stack authenticated and clean, and treat remaining uncertain results as decisions to manage, not failures to hide.
Greylisting is when a receiving mail server temporarily rejects a message from an unrecognized sender–recipient–IP combination with a 4xx “try again later” response. A legitimate sending server retries and is usually accepted after enough time has passed.
In validation, anti-greylisting means the verifier waits and retries SMTP mailbox checks when a provider returns a temporary greylist-style deferral. The goal is fewer false inconclusive “unknown” results — risk reduction, not bypassing spam filters for marketing sends.
Greylist windows often last several minutes. Retrying after that delay adds processing time — commonly on the order of 30–60 minutes for affected jobs — in exchange for clearer valid/invalid outcomes on greylisted addresses.
No. Some domains are catch-all, throttled, tarpitted, or configured to block probes. Anti-greylisting helps with temporary deferrals; it does not remove all technical limits of SMTP-based verification.
Keep uncertainty when the domain is catch-all, when the provider still defers or blocks after retries, or when responses stay inconsistent. Residual unknowns are better handled with a risk policy than forced valid/invalid labels.
Authenticate with SPF, DKIM, and DMARC, maintain clean lists and low complaint rates, send on a consistent pattern, and warm new domains or IPs gradually. Looking like a trustworthy sender reduces how often first-contact mail is deferred.
No. Greylisting is a temporary deferral for unfamiliar connections. A blacklist or blocklist is a stronger reputation or policy block that typically requires remediation, not just waiting and retrying once.
Find quick answers to your questions about our pricing and plans.
Mail merge allows you to combine a message template with a structured data source to create personalized communications at scale. Mail merge works...

Mass emailing is a powerful way to communicate a message to a large audience. The goal could be anything from boosting conversions, a quick follow-up...

Yahoo Mail and AOL (Yahoo-hosted consumer brands) enforce bulk-sender standards: SPF and DKIM, a DMARC policy of at least p=none that passes with...
There are two types of emails you can send to your customers: transactional emails and marketing emails. If you want to get the most out...
Email lists are the foundation for an effective email marketing campaign. Building an email list is ongoing for as long as you need it to....


Skipping warmup on a new domain or IP often leads to throttling, spam placement, or blocked delivery. Strong warmups depend on clean lists,...